
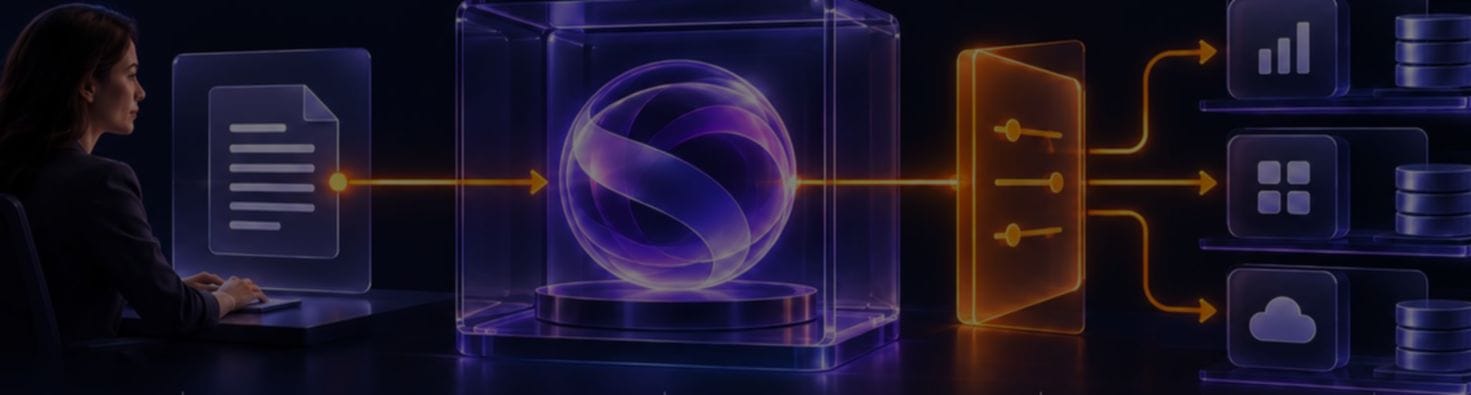
Where data lives, what an agent may do, who approves.
A task with an owner, an agent in a defined environment, controls over access and actions, approved target systems. We separate what runs today from what is planned.
Workflow
A task with an owner.
Agent
Runs in a defined environment, locally or in the partner's data center.
Control
Permissions, budgets and approvals, every step in the trail.
Systems
Approved access to your systems, nothing beyond it.
Conceptual architecture, not a verified implementation diagram.
Implemented today, planned, in development. Stated separately.
For each control we state what KIONOVA gateway delivers today and what is in development with QUORIXX.
| Control | Today (KIONOVA gateway) | In development (QUORIXX, concept) |
|---|---|---|
| Data location | Data classes per request. Strict goes only to local models, confidential is rerouted. Contents are not stored by default. | Secrets and credentials outside the agent environment, release only for narrowly scoped access. |
| Identity | Virtual key per workplace, stored only as a hash, revocable. Administration with roles and its own login. | Separate identities for request, evaluation, approval and execution. One identity must not hold all three roles. |
| Tool permissions | Model allowlist, token caps, rules per role. Tool calls are observed and recorded. | Enforcement per tool call before execution, at a protected execution point. |
| Approvals | Allow, ask, deny. Requests with ask wait for a person with role and right. | Action-bound approval with target, parameters, scope and expiry. Quorum from independent roles for high risk classes. |
| Logging | Flight recorder: chained trail with time in the hash, anchored with a timestamp service and a WORM sink, signed run receipts, open verifier. | Evidence layer outside the agent's reach, export to external, immutable systems. |
| Exceptions | Provider errors pass unchanged. An exhausted budget rejects. A client abort stops the call. | Fail closed: if a control is unreachable, the protected action does not take place. |
| Shutdown | Revoke keys and workplaces, set rules to deny, administration separated from the proxy. | Revocation of approvals and credentials per action, emergency access with a record. |
KIONOVA® gateway
AvailableThe enforceable point in the picture: access, permissions and evidence in one place.
- Position in the architecture: action gateway, policy engine and evidence layer (flight recorder).
- Permissions, budgets and approvals per workplace, for both common API dialects.
- The flight recorder makes every step verifiable offline and provides auditable evidence for the AI Act, DORA and GDPR.
- Operated as part of the joint delivery solution with BrainQubes.
From the data center into the company. Every link with its security argument.
Data center
BrainQubes: modular AI data centers in Europe, dedicated hardware, operated under European control.
Models
Run there or locally at the customer. The data class decides which provider may see a request.
KIONOVA® gateway
The single access point for the company. Provider keys stay in the vault, workplaces get virtual keys.
Workplaces
SEPP, sepp mini, your own applications and developer tools speak their usual dialect.
Evidence
Chained, anchored, offline verifiable trail. Auditors verify without the vendor.
QUORIXX
ConceptAction control for AI agents. No quorum. No action.
QUORIXX is a product concept initiated by BrainQubes and under evaluation. An independent control layer evaluates a specific action before execution and allows it, denies it or requires approval from designated people or systems. The AI may request an action. It cannot grant itself authority.
KIONOVA is proposed as a technology contribution: integration into AI workflows, exposing actions at enforceable points, connecting tool use to the control path.
Target architecture in seven stages
AI agent
Proposes an action: API call, query, file change, process, connection.
Action Gateway
Controlled entry point, normalises the request, prevents direct access.
Policy Engine
Assesses identity, purpose, target, data class, parameters, context. Assigns a risk class.
Approval Service
Collects approvals tied to an immutable action record with expiry.
Secret Broker
Credentials never rest with the agent. After a valid decision a short-lived, narrowly scoped token.
Execution Gateway
Rechecks decision, token, parameters and expiry immediately before execution.
Audit Layer
Requests, policies, approvals, credential release and execution, outside the agent's reach.
The central rule: QUORIXX controls the action that is about to be executed, not merely the AI system's stated intention.
Risk classes
| Class | Examples | Decision |
|---|---|---|
| Low | Read non-sensitive information, use an approved tool. | Allowed automatically within defined limits. |
| Medium | Internal data, altering non-critical systems, communicating externally. | Approval by an accountable person or a defined service. |
| High | Secrets, production, personal data, finance, identity systems. | Independent multi-stage approval or quorum. |
| Prohibited | Actions outside the permitted business and security model. | Always blocked, regardless of the agent's explanation. |
Design principles
Fail closed
If a control is unavailable, the protected action does not take place.
Least privilege
Only the tools and rights the task needs. No admin keys with the agent.
Action-bound approval
Single-use or short-lived, only for exactly this action record.
Independent duties
Request, evaluation, approval, credentials and execution in separate identities.
Protected evidence
The agent cannot delete or rewrite records.
No direct bypass
Network, identities and permissions make the controlled path the only practical one.
Independent quorum
Several approvals from distinct roles and trust domains.
QUORIXX is a product concept under evaluation, initiated by BrainQubes. The first milestone is a limited prototype that proves four properties: no bypass of the protected execution path, no access to protected credentials without approval, no reuse of an approval for a different action, no alteration of the evidence record. Any claim of universal attack prevention would be premature. The aim is a measurable security boundary whose coverage and gaps can be tested independently.
According to the concept paper, fragmentiX is proposed as a further technology contribution.
Discuss the architecture?
We show the control path on a real call: decision, record, execution, verification.